Launch delayed one week: the course will be ready on 30 October.
Contractor obligations (PHP and certificate issues) landed in the final week of course preparation. Everyone who has registered keeps free lifetime access.
Free course · OWASP 2017, 2021 and 2025 · Live 30 October
F5 ASM: OWASP Top 10 Essentials
Understand how real web application attacks work and how F5 ASM detects and mitigates them.
Covers OWASP 2017, 2021 and 2025, because older OWASP risks still matter in legacy applications. Every attack is demonstrated using VS Code, Postman and F5 ASM, not just slides.
A must-take course for anyone working with F5 ASM who wants a deeper understanding of the OWASP Top 10.
Register before 30 October and the course is yours for life, free.
I'm Graham Mattingley: 18 years of real-world F5 experience, ASM in production the whole way, and 30 years across security and development.
Register for OWASP Top 10 Essentials
The course goes live on 30 October. Register now and you get free lifetime access when it does.
The outcome
You will leave this course OWASP-competent. Not OWASP-aware.
Eighteen years inside F5's biggest customers and thirty building the applications they run have given me a clear picture of how large organisations actually operate: who raises the alarm, who gets blamed, who has to explain. Every risk in this course is taught the way it shows up there, under pressure, with people waiting for an answer.
When a CVE lands, say a PHP remote-code-execution bug with a working web shell, you will be able to:
- Read it and say exactly what it does to the application
- Link it directly to the ASM mitigations that stop it, and apply them
- Explain what you did and why, in security language, to the people who sign it off
- Explain the same thing in application language to the developers who have to fix the root cause
Do that a few times where you work and you become the person they ask first. That is a much stronger position to be in, whatever the market is doing.
F5 ASM
Fully competent
Full understanding of how to mitigate each OWASP risk in ASM.
The application
High-level understanding
Full understanding of where in the application the issue needs to be resolved.
OWASP
Fully competent
Full understanding of the risks: what they are, how they're exploited, why they matter.
To be clear: this is an OWASP course that uses ASM, not an ASM course. The full F5 ASM course, mapped to the 303 blueprint, follows very soon.
Real attack demonstrations
See how OWASP attacks work using VS Code, Postman and F5 ASM. Sent, caught, explained.
F5 ASM protection
Understand how F5 ASM detects and blocks common web attacks, and watch the violations fire on a live policy.
Practical security
Learn how OWASP vulnerabilities appear in real applications and how they map to WAF/ASM protection and application security controls.
Inside the course
Animated slides for the concept. The real BIG-IP for the practice.
Every lesson follows the same pattern: a short animated slide explains the risk, then I switch to a live ASM policy on the lab BIG-IP and show you the attack, the signature and the block. Here's what that looks like.
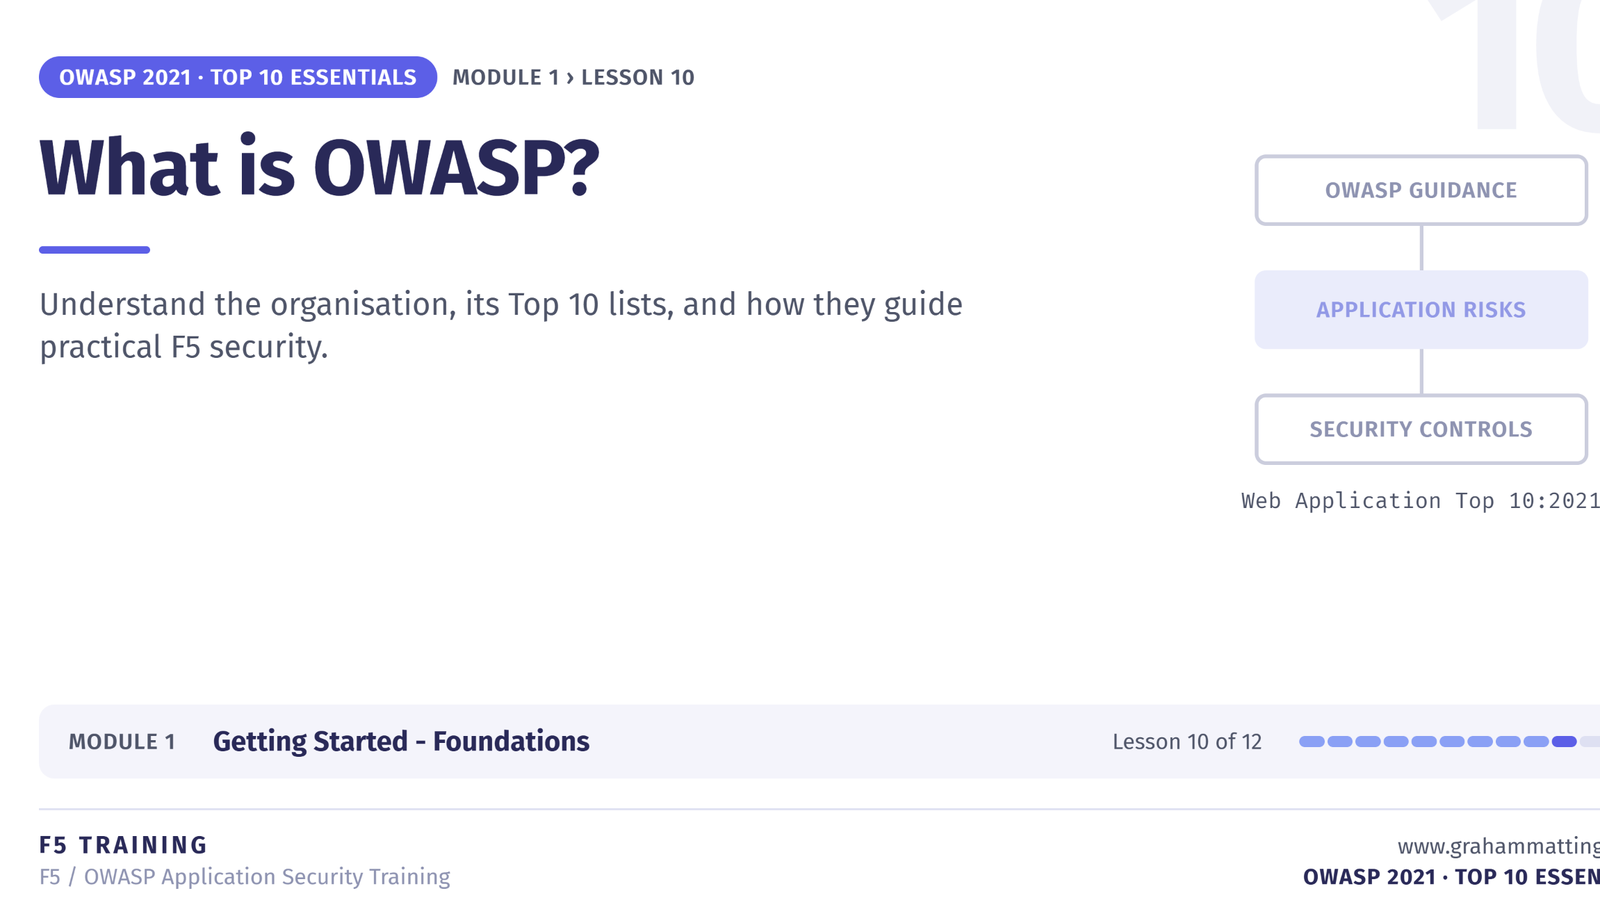
Every lesson starts here
A title slide that places the lesson in the module and tells you what you'll be able to do by the end of it.
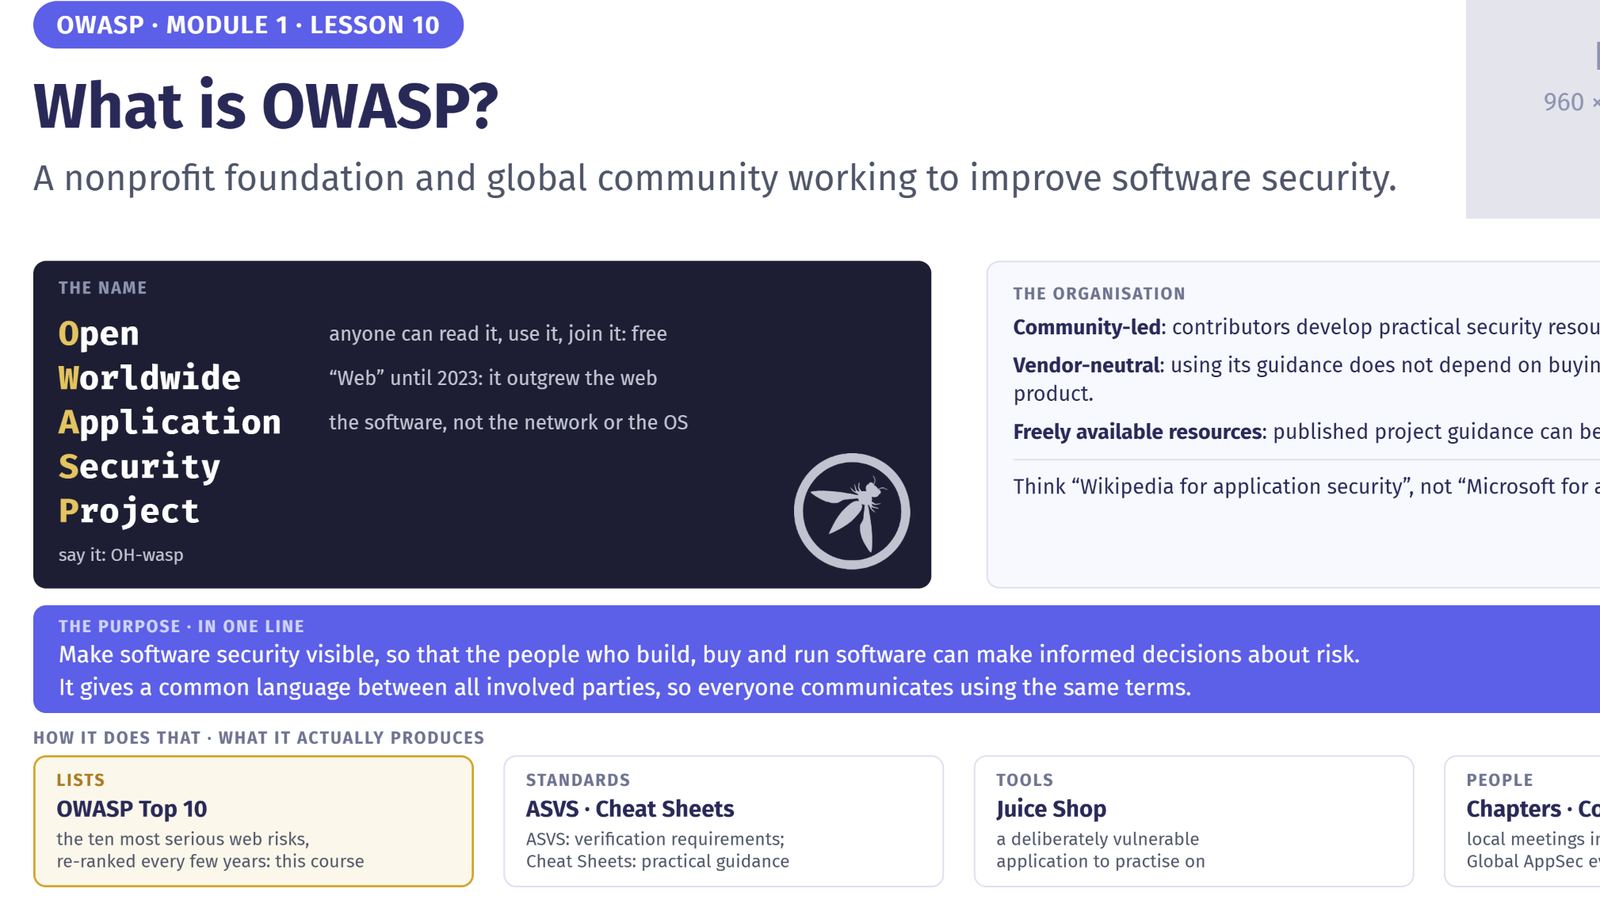
The concept, animated
Slides built for this course, not stock decks. Each one builds up on screen as I talk, so the idea lands before I touch the box.
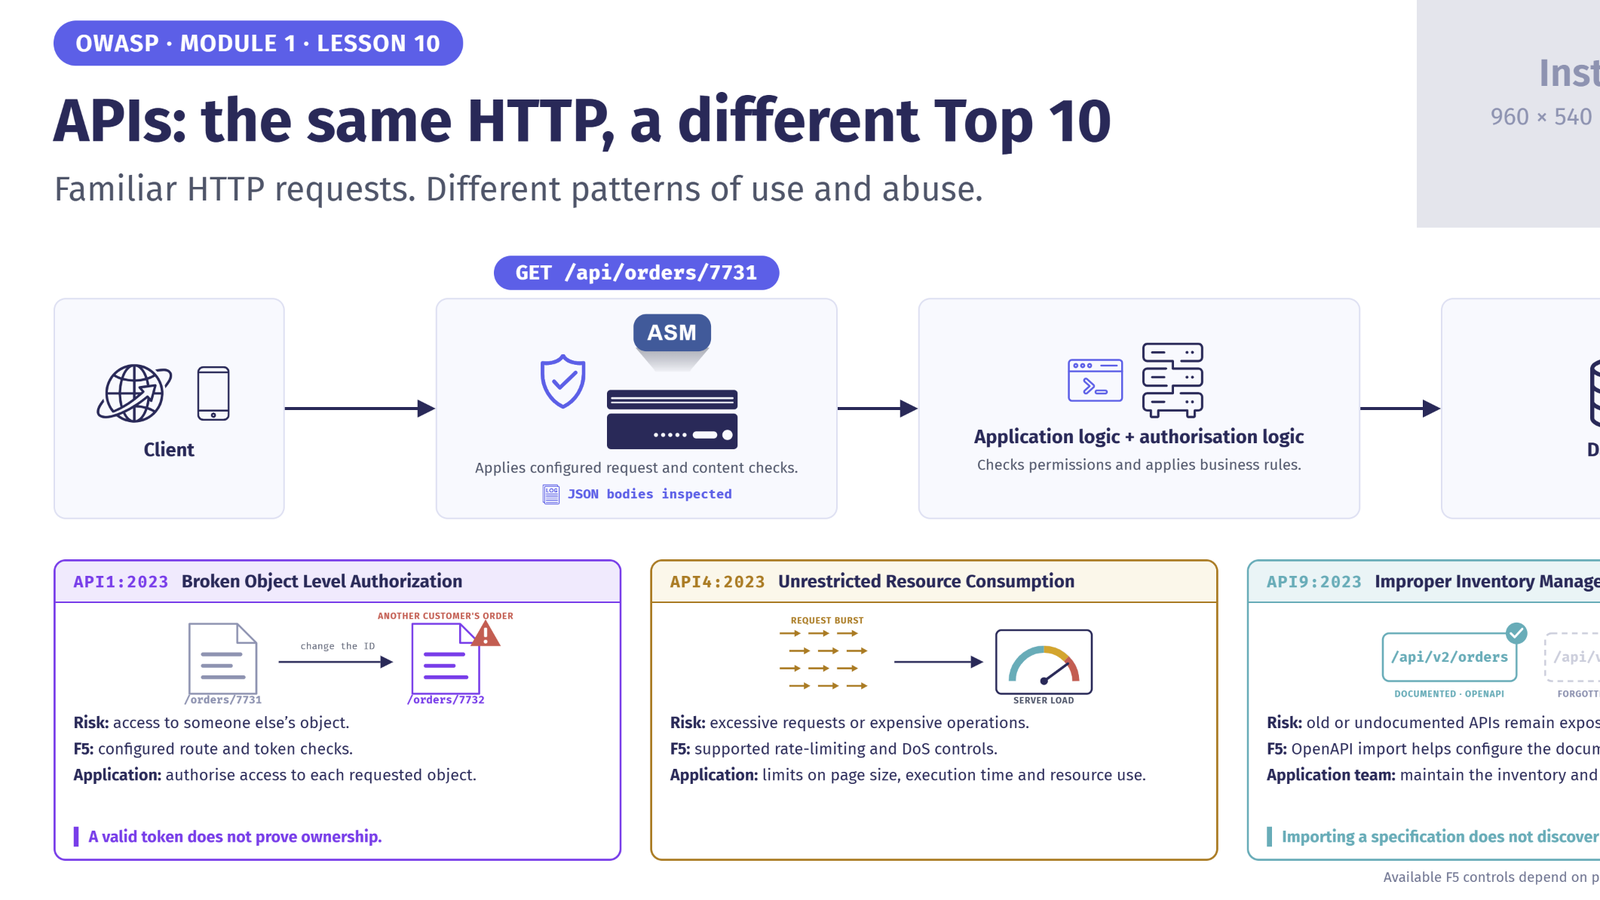
APIs get their own Top 10
Where ASM sits in the request path, what it can check, and what the application still has to do itself. Both sides, every time.
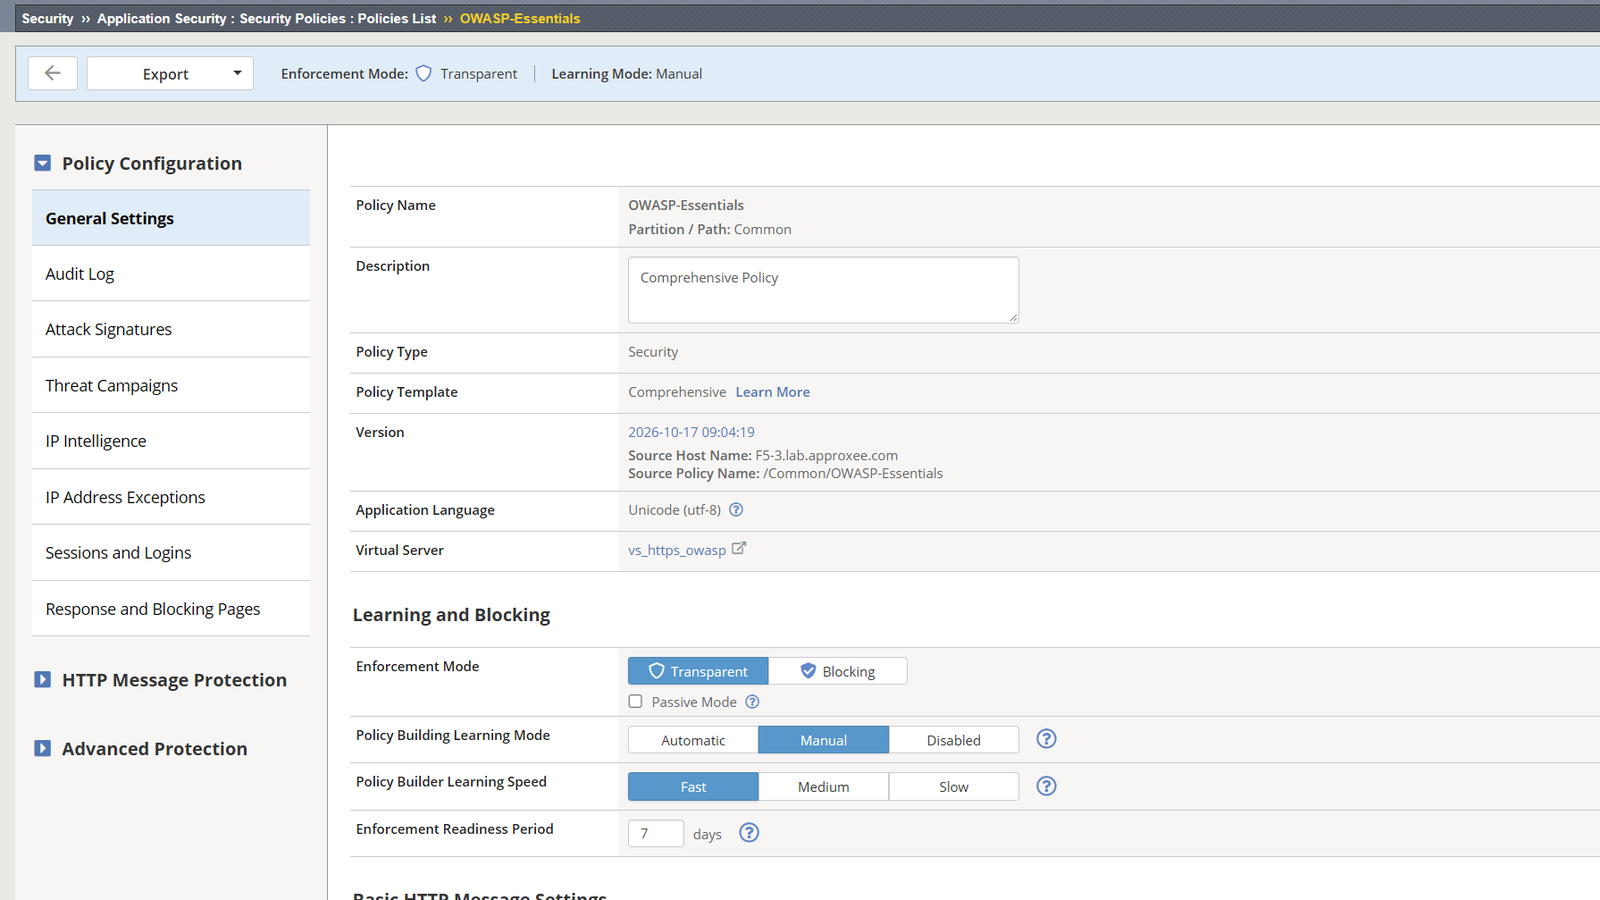
A real policy, built for the course
The OWASP-Essentials policy on the lab BIG-IP: enforcement mode, learning mode, readiness period. You watch it go from transparent to blocking.
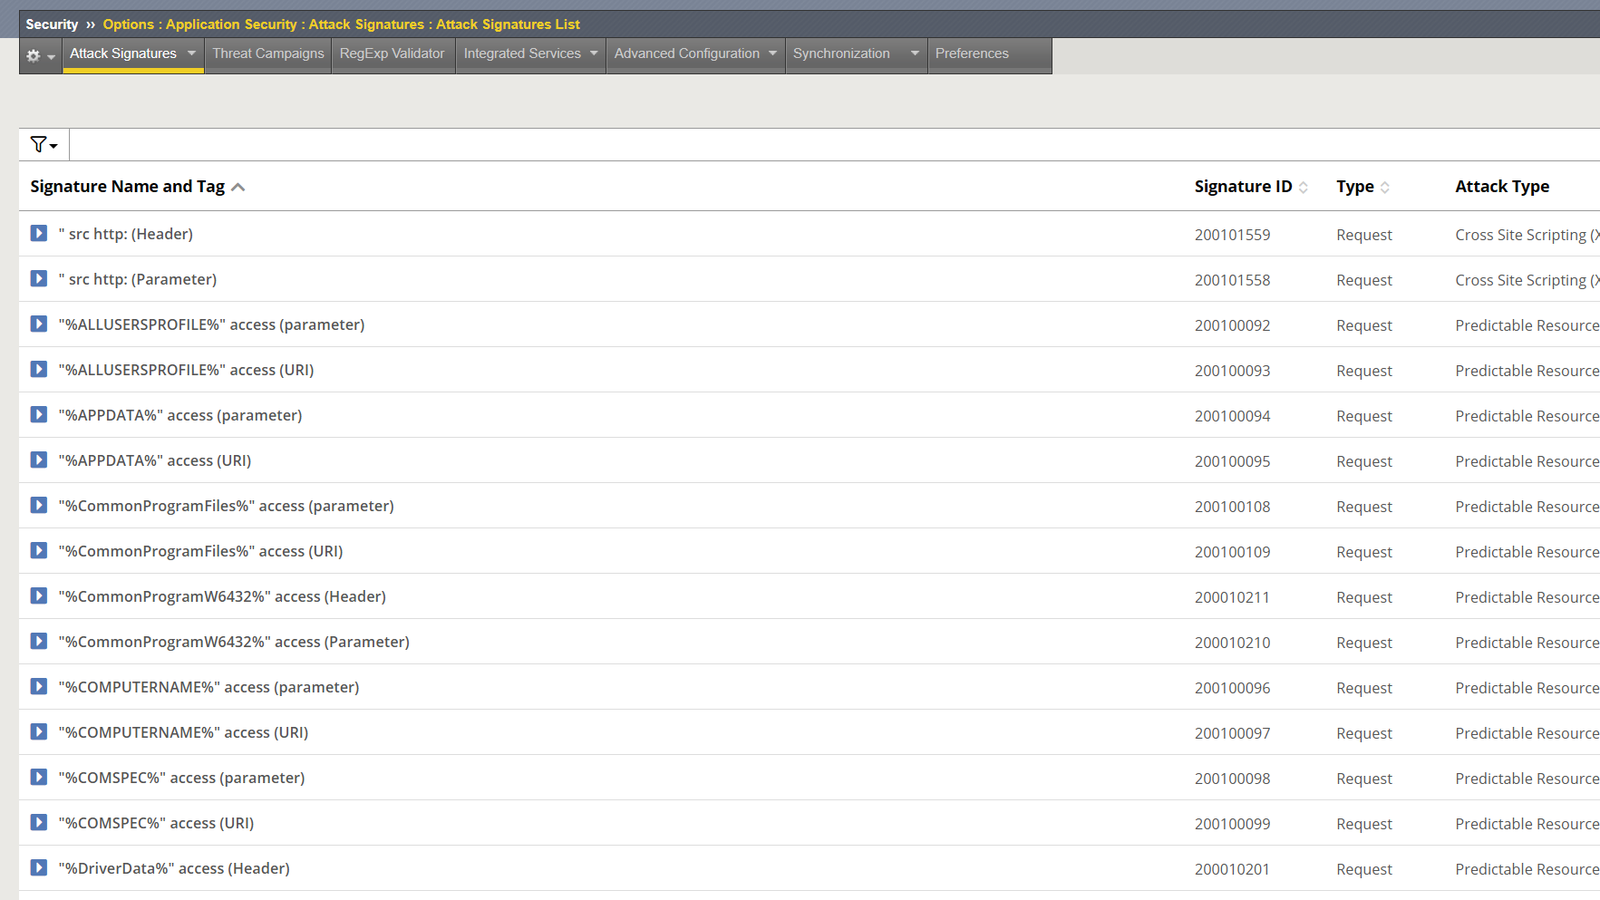
9,509 attack signatures
Which ones map to which OWASP risk, what accuracy and risk actually mean, and how to tell a real hit from a false positive.
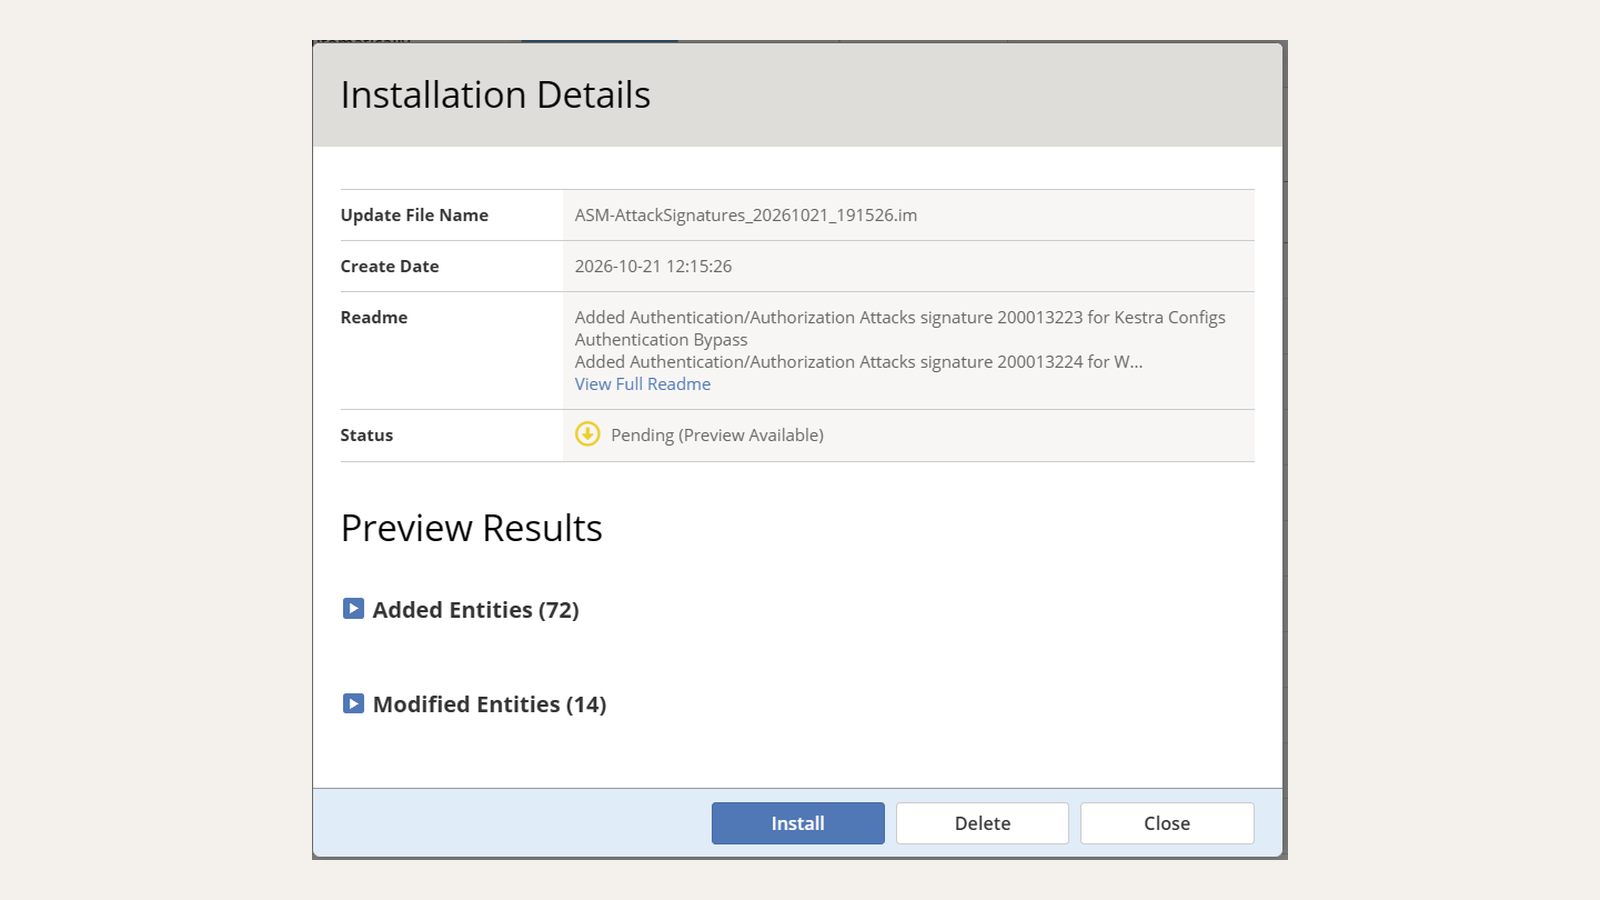
Keeping the signatures current
Signature updates arrive every few days. What's in them, how to preview before you install, and why staging matters.
What you get
Understand the OWASP Top 10 in a real F5 ASM environment
Learn how common web application attacks work and how F5 ASM detects and mitigates them in practice.
I explain each OWASP Top 10 vulnerability and how it appears in real applications, then demonstrate it using VS Code, Postman and F5 ASM: sent, caught, explained.
A practical course designed to improve your understanding of OWASP and strengthen your skills working with F5 ASM.
Built from 18 years of deploying and troubleshooting F5 ASM in production environments, and 30 years of writing the applications it protects.

FAQs
Before you ask
Who is this course for?
What makes this course different from other OWASP courses?
What do I get if I register before 30 October?
Why is lifetime access free for early registrants?
Register for OWASP Top 10 Essentials
Live on 30 October. Register now and you get free lifetime access when it goes live.